Medical Testing Giant Quest Diagnostics Confirms Massive Security Breach Exposing Sensitive Patient Records Amid a Coordinated Global Hacking Surge
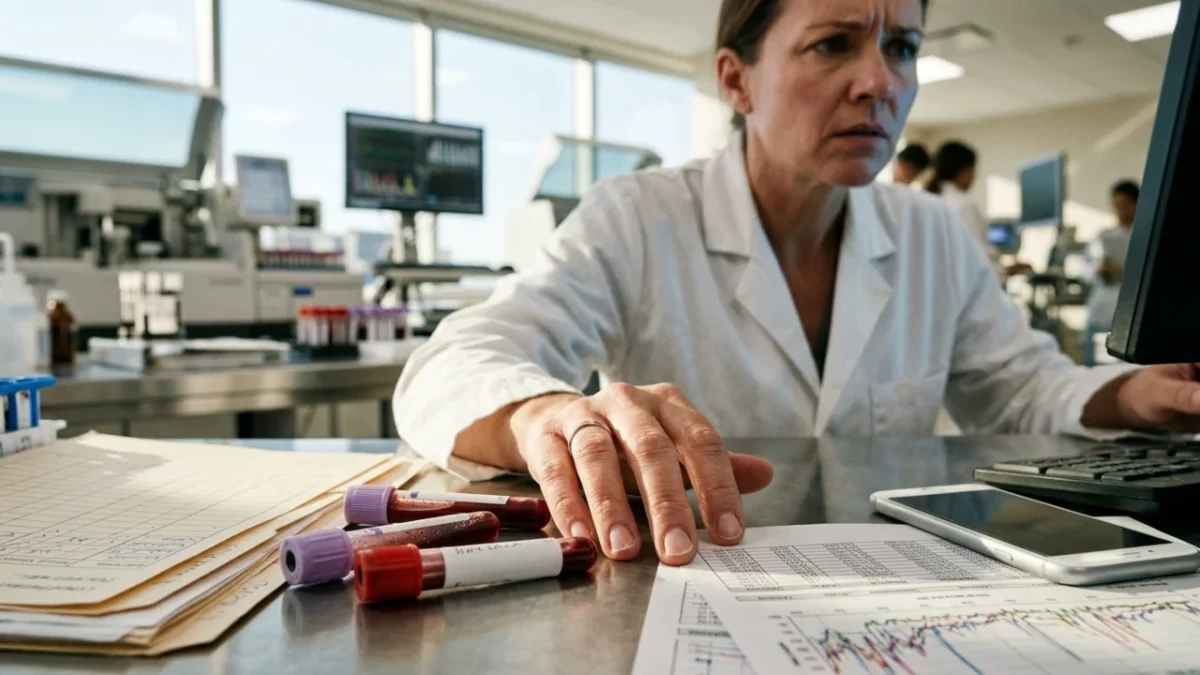
Healthcare titan Quest Diagnostics has officially confirmed that unauthorised intruders infiltrated its central laboratory management platform, compromising sensitive patient records and confidential medical data across the United States. The intrusion struck the company’s vital Quanum Lab Services Manager system, the exact digital hub that doctors, hospitals, and medical clinics utilise every day to commission bloodwork and review laboratory findings.
The disclosure has ignited urgent privacy alarms across the medical sector. While federal investigators and external forensic specialists work to trace the intrusion, company officials have conceded that protected health information and personally identifiable data were accessed by an unknown third party.
The revelation marks a severe escalation in what technology executives are now describing as an unprecedented wave of digital exploitation.
The Breach at Quanum: How Patient Health Data Was Compromised
According to formal regulatory disclosures filed with the U.S. Securities and Exchange Commission, Quest Diagnostics uncovered the unauthorised intrusion on Wednesday, 21 October. Regulators received formal notification the following day, before the diagnostic group acknowledged that private records had been accessed.
By Friday, 23 October, the company upgraded the severity of the alert, confirming that protected health information and personal identity details were caught in the net. Despite those admissions, investigators have yet to establish the total number of individuals impacted or the specific clinical categories of records exposed.
The breach targets the nerve centre of routine medical testing. The compromised platform enables clinicians to manage diagnostic orders, communicate test requests, and review private laboratory results directly from their practices.
Quest Diagnostics moved swiftly to contain the perimeter by severing access to the compromised Quanum platform. As a precautionary measure, the firm also temporarily halted operations across secondary systems, including Essential Insights and LabHQ, though it reported no direct infiltration within those specific networks.
Doctors relying on the platform were immediately redirected to paper requisitions and alternative digital interfaces to maintain laboratory services. While the testing provider maintains that core diagnostic operations continue without material disruption, serious questions remain regarding how long intruders held access before discovery.
Compounding patient frustration, Quest Diagnostics placed a “noindex” directive within the coding of its official online security statement. The command prevents standard internet search engines from indexing the notice, making the alert considerably harder for affected patients to locate through ordinary digital searches.
Identity Theft, False Insurance Claims, and the FTC Warning
The fallout from compromised health records extends far beyond private diagnostic confidentiality. The Federal Trade Commission has warned that stolen healthcare records represent high-value currency in complex identity fraud schemes.
Fraud syndicates routinely deploy compromised diagnostic data to submit fraudulent medical claims, bill insurers for fictitious treatments, or obtain prescription pharmaceuticals under an innocent patient’s name. When falsified medical events merge with authentic clinical histories, the corrupted records can pose dangerous complications for future emergency care.
To defend against secondary exploitation following a Quest Diagnostics breach, security authorities advise taking immediate precautions:
- Scrutinise healthcare billing statements: Review explanation of benefits summaries carefully for unfamiliar medical consultations, unexplained laboratory fees, or duplicate testing procedures.
- Reject unverified medical communications: Never surrender national insurance identifiers, policy numbers, or personal health records to unsolicited telephone callers or unauthenticated text alerts.
- Cross-check diagnostic notices directly: If contacted regarding unexpected bloodwork or clinical findings, verify the message independently through official medical practice switchboards rather than embedded email links.
‘Black October’: An Escalating Crisis Across Global Infrastructure
The compromise at Quest Diagnostics unfolds alongside what cybersecurity leaders are calling “Black October”—a devastating period marked by the automated discovery and weaponisation of fundamental software vulnerabilities. On 21 October, security researchers revealed catastrophic flaws within the PHP programming language, a bedrock technology powering an estimated 70 percent of websites worldwide.
Researchers at the AI security platform Wiz characterised the defect as one of the most severe in software history, observing that while the flaw lay dormant for decades, discovering it required an intricate chain of operations that pushed human engineering to its limits.
Following the public alert, government portals and enterprise systems in both the US and the UK temporarily went offline to implement emergency patches. The U.S. National Security Agency warned that malicious operators are actively seeking to exploit the vulnerability to hijack internal servers, disrupt public services, and siphon protected data.
A Rapid Tsunami of Automated Cyber Attacks
Technology executives are warning that the nature of cyber conflict has permanently shifted. Cloudflare Chief Executive Matthew Prince revealed that automated attempts to exploit the newly exposed programming flaws surged from thousands of daily probes to hundreds of thousands within two hours of public disclosure, quickly rocketing into millions.
The unprecedented velocity of these attacks is straining digital defences to breaking point. Anthropic Deputy Chief Information Security Officer Jason Clinton warned that global networks are entering a “vulnerability tsunami” where system administrators will lack the time required to shield critical infrastructure.
Salesforce Chief Executive Marc Benioff designated the sweeping exposure a “code red”, while OpenAI Chief Executive Sam Altman openly conceded that developers may no longer be able to patch all emerging flaws as automated discovery tools evolve.
The healthcare supply chain remains uniquely exposed to this pressure. Only months prior, medical device manufacturer Boston Scientific suffered global operational disruption following an aggressive cyber incident, demonstrating that the operational technology sustaining modern healthcare is under sustained siege.
💡 As enterprise networks race to construct automated defences against this new wave of intrusions, consumers must treat any unexpected communication demanding medical verification with deep scepticism.
🔍 The combination of industrial software vulnerabilities and targeted attacks against health management systems signals a challenging era for patient privacy and institutional security.
👇 Have you encountered unexpected medical correspondence or suspicious insurance notifications following recent lab work? Share your perspective in the comments below.
 1
 2
 3
 4